What is DevSecOps?
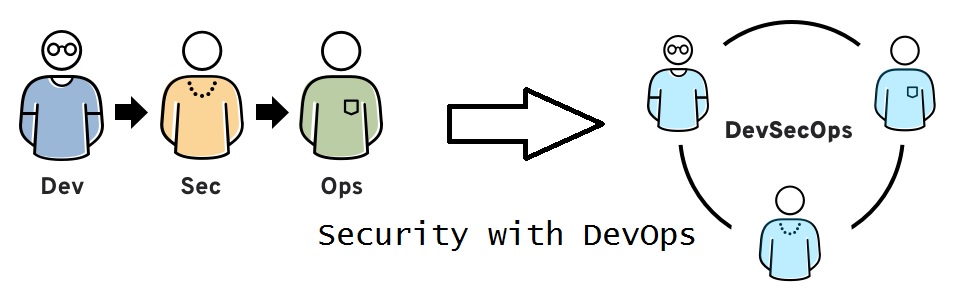
DevSecOps is the philosophy of integrating security practices within the DevOps process. DevSecOps involves creating a ‘Security as Code’ culture with ongoing, flexible collaboration between release engineers and security teams. The DevSecOps movement, like DevOps itself, is focused on creating new solutions for complex software development processes within an agile framework.
Why Security?
From scans of over 31,000 sites, over 85% showed a vulnerability that could give hackers the ability to read, modify and transmit sensitive data. [Web Application Security Consortium].
Why DevSecOps?
“80% of Malicious Attacks happen at the application layer”. –[Gartner]
DevOps Security Best Practice Approach
- Quickly find and remediation of critical vulnerabilities
- Don’t “forget to fix” or “boil the ocean”
- Prevent introduction of new vulnerabilities
- Integrate into existing SDLC with minimal process changes
- Provide flexibility to integrate with new SDL as it rolls-out
- Provide support for the developers
- Training in the context of their own code base
- Mentoring as required
- Monitor and control
- Automate gathering of vulnerability statistics and publish
- Enforcement via security gate
- Continuous Improvement
Agenda of DevSecOps Course Training are as follows;
- What is Security?
- Why Security?
- What is DevSecOps
- Understanding a types of Threat in DevOps
- Why DevSecOps?
- DevOps Security Best Practice Approach
- Understanding a Phases in DevOps and Their Security Concern
- Recommendations for Security Practices in DevSecOps
- Recommendations for Security Tools in DevSecOps
- DevOps Security Phases
- Static Application Security Testing (SAST)
- Dynamic Application Security Testing (DAST)
- Runtime Application Security Testing (RAST)
- Database Security Scanning
- Mobile Application Security Testing (MAST)
- DevSecOps Practices with AWS
- DevSecOps Practices with Docker
- DevSecOps Practices with Kubernetes
- Implementing some of the DevSecOps Tools
- OWASP SonarQube for Code Scanning [Demo]
- Chef InSpec for Scanning your applications and infrastructure[Demo]
- ELK with Kibana for Log analysis for Security Threat[Demo]
- HashiCorp Vault for security tool for certificates, API keys, or passwords [Demo]
- Fortify Webinspect for Dynamic Application Security Testing (DAST) [Demo]
- Fortify Application Defender for Runtime Application Security Testing (RAST)
Please contact Contact@DevOpsSchool.com for more information about this course and Training.

I’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked at Cotocus and regularly write about technology, travel, investing, health, product reviews, and digital marketing through my various platforms.
I publish technical articles at DevOps School, travel stories at Holiday Landmark, stock market insights at Stocks Mantra, health and fitness guidance at My Medic Plus, product reviews at TrueReviewNow, and SEO and digital marketing strategies at Wizbrand.
Find Trusted Cardiac Hospitals
Compare heart hospitals by city and services — all in one place.
Explore Hospitals