
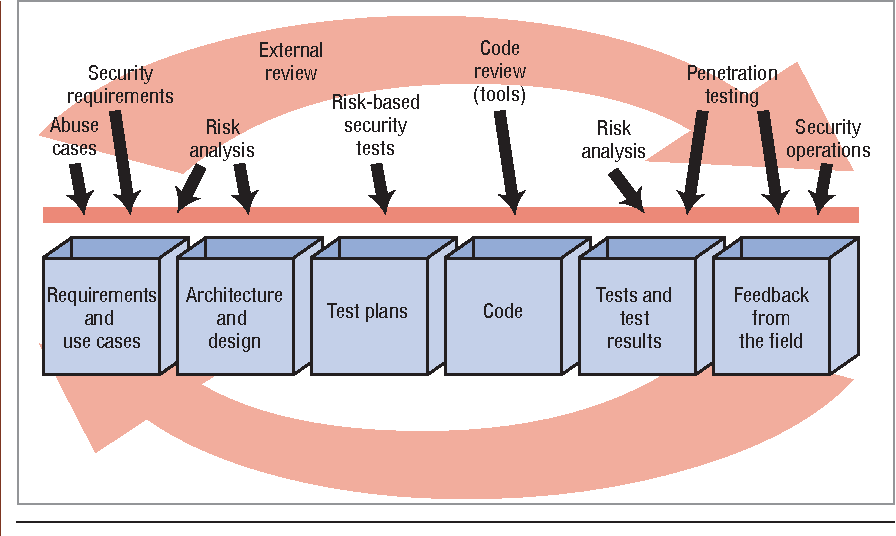
The following are the best security code review tools:
- SonarQube: SonarQube is a popular open source code quality and security analysis platform. It supports over 27 programming languages and can scan for a wide range of security vulnerabilities, including SQL injection, cross-site scripting (XSS), and buffer overflows.
- Checkmarx: Checkmarx is a commercial code security analysis tool that supports over 30 programming languages. It uses a variety of static analysis techniques to identify security vulnerabilities, including data flow analysis, control flow analysis, and taint analysis.
- Fortify Static Code Analyzer: Fortify Static Code Analyzer is a commercial code security analysis tool that supports over 25 programming languages. It uses a variety of static analysis techniques to identify security vulnerabilities, including data flow analysis, control flow analysis, and memory analysis.
- OWASP Dependency-Check: OWASP Dependency-Check is an open source tool that scans for known vulnerabilities in open source dependencies. It can be used to scan for vulnerabilities in dependencies used in Java, Python, Ruby, and other programming languages.
- PractiTest: PractiTest is a commercial test management tool that also includes a code review feature. It supports over 20 programming languages and can be used to automate code reviews.
These are just a few of the many security code review tools available. The best tool for you will depend on your specific needs and requirements.
Some factors to consider when choosing a security code review tool:
- The programming languages you use: Make sure the tool supports the programming languages you use.
- The types of security vulnerabilities you want to find: Some tools are better at finding certain types of vulnerabilities than others.
- The size and complexity of your codebase: Some tools are better suited for large and complex codebases than others.
- Your budget: Security code review tools can range in price from free to thousands of dollars per year.
- Your team’s experience with security code review: If your team is new to security code review, you may want to choose a tool that is easy to use.
👤 About the Author
Ashwani is passionate about DevOps, DevSecOps, SRE, MLOps, and AiOps, with a strong drive to simplify and scale modern IT operations. Through continuous learning and sharing, Ashwani helps organizations and engineers adopt best practices for automation, security, reliability, and AI-driven operations.
🌐 Connect & Follow:
Website: WizBrand.com
Facebook: facebook.com/DevOpsSchool
X (Twitter): x.com/DevOpsSchools
LinkedIn: linkedin.com/company/devopsschool
YouTube: youtube.com/@TheDevOpsSchool
Instagram: instagram.com/devopsschool
Quora: devopsschool.quora.com
Email– contact@devopsschool.com
Find Trusted Cardiac Hospitals
Compare heart hospitals by city and services — all in one place.
Explore Hospitals





This is a really useful list of top security code review tools! I like how the article highlights each tool’s strengths — it makes comparing and choosing the right one much easier. Thanks for sharing these helpful insights!