
Network slicing is the ultimate key to unlocking 5G performance for the 3 million DevOps professionals working in teams worldwide by carving a physical network into multiple virtual pipelines tailored to specific application needs. Instead of treating the network as a dumb, shared pipe, engineering teams can now treat connectivity as code. This shift allows you to deploy high-throughput, low-latency containerized network functions directly alongside your application microservices.
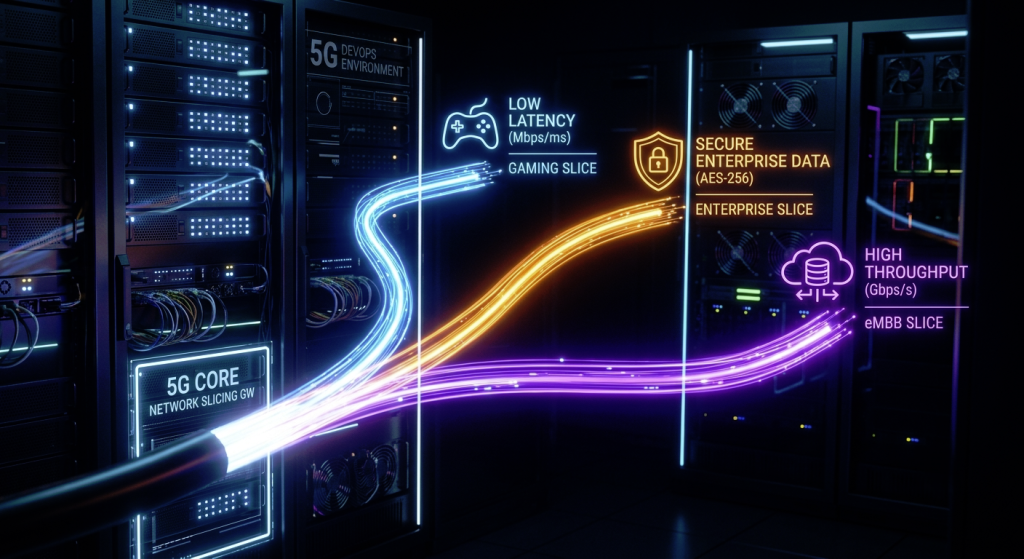
How Network Slicing Redefines Cloud Native Infrastructure
Modern development relies on rapid deployment cycles and highly predictable environment behaviors. When containerized network functions run on Kubernetes, they must dynamically interact with the radio access network and the core infrastructure. Managing these complex interfaces requires tools like GitOps principles using Flux CD to automate configuration and maintain policy as code across every slice.
By treating network slices as dynamic resources, DevOps engineers can prevent network-level bottlenecks from breaking application service-level objectives. You no longer have to hope the network behaves under peak load because you can configure a dedicated slice to handle your critical API traffic routed through your carefully selected gateway. This capability shifts the boundary of application control to the edge of the carrier network.
Bridging the Gap Between Code and Telecom Hardware
Historically, developers had no control over the cellular networks that transmitted their data packets. With 5G network slicing, you can manage bandwidth, latency, and security policies as easily as you provision an AWS or Azure virtual machine.
Service providers like Optus are facilitating this transition by delivering high-speed, localized consumer experiences that demand robust monitoring from development teams. That’s why picking the right provider matters as much as getting to grips with network slicing itself.
Integrating these capabilities requires a massive cultural shift in how we approach telemetry. There are hundreds of thousands of automated microservice deployments every day in modern telecommunication networks. To keep pace with this velocity, engineering teams must implement continuous integration and closed-loop management to verify that network slices spin up and self-heal in real time.
Essential Metrics for Monitoring Slice-Aware Applications
To successfully run applications on dedicated slices, your observability stack must evolve past standard CPU and memory metrics. You need real-time visibility into slice isolation, packet loss, and jitter directly from the container runtimes. The following checklist details the primary areas your development team must continuously monitor to maintain optimal performance:
- Kubernetes pod networking latency across the RAN core
- Dynamic bandwidth allocation thresholds during high-traffic events
- Cross-slice isolation boundaries to prevent resource starvation
If a slice fails to deliver its promised quality of service, your automated pipelines must trigger chaos engineering tests to validate fallback mechanisms. These automated test suites ensure your application gracefully downgrades to standard 5G networks without causing downtime for the end user. This level of automated resilience is what separates average cloud-native deployments from true next-generation telecom integrations.
Enhancing Security With Slice Isolation Policies
Zero-trust security models are no longer optional when deploying modern applications. Implementing slice isolation and zero-trust policies prevents data leakage between different virtual networks operating on the same physical infrastructure. These architectural boundaries protect sensitive enterprise workloads from being compromised by public internet traffic.
DevOps teams can define these security policies directly within their CI/CD pipelines. This automation ensures that every microservice is automatically mapped to its designated secure network slice during deployment. Consequently, security compliance becomes a seamless, automated step in your standard release cycle.
How to Get Started With Slice-Aware DevOps
Transitioning to a slice-aware development model begins with evaluating your current infrastructure automation tools. You must ensure your orchestration platforms can communicate directly with telecom APIs to request and configure slices on demand. Reading our guides on modern DevOps topics can help you build the skills necessary to master these complex integrations.

I’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked at Cotocus and regularly write about technology, travel, investing, health, product reviews, and digital marketing through my various platforms.
I publish technical articles at DevOps School, travel stories at Holiday Landmark, stock market insights at Stocks Mantra, health and fitness guidance at My Medic Plus, product reviews at TrueReviewNow, and SEO and digital marketing strategies at Wizbrand.
Find Trusted Cardiac Hospitals
Compare heart hospitals by city and services — all in one place.
Explore Hospitals
Network slicing can help DevOps teams match network performance to each application’s needs. The real benefit comes when teams can monitor latency, bandwidth, and reliability for each slice in real time. Linking these metrics to deployment alerts can help spot issues before users notice them. Teams should also test how slices behave during traffic spikes and network failures. Clear service targets and automated recovery plans can make sliced networks easier to manage at scale.
One operational challenge worth considering is lifecycle drift between the DevOps control plane and the telecom network. A slice can look correctly configured in Git while the provider-side state, capacity, or QoS behavior has changed underneath it. Reconciliation, explicit ownership, slice-level SLOs, and well-tested fallback policies would be important here, especially when applications depend on a specific latency or bandwidth guarantee in production.