
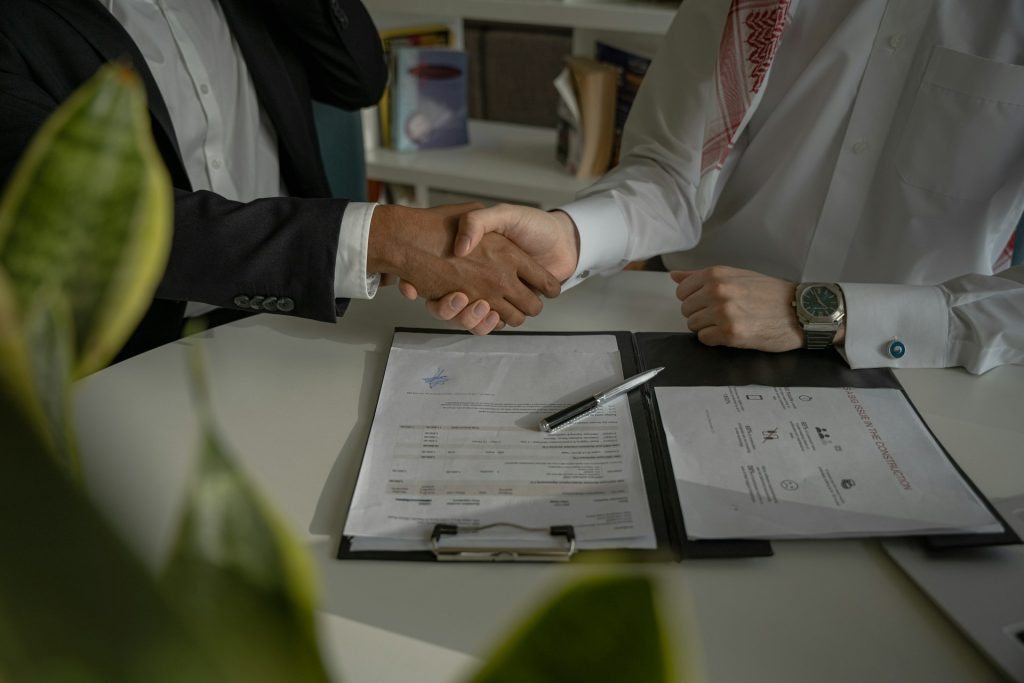
DevOps teams rely on specialized SaaS tools to automate, monitor, and scale software development and delivery processes. These platforms reduce manual effort, minimize human error, and help teams release software faster.
Because these solutions are cloud-based, someone else handles the maintenance, updates, security patches, and service availability. It’s so development teams can focus on building and shipping software.
Pretty convenient right? Only, there’s a catch: the contract and terms you agree to when you start using a new vendor and their tools can hide risks in plain sight. Overlooking them can lead to unexpected vendor lock-in costs, pipeline disruptions, compliance issues, or even exposure of proprietary code and system data.
To avoid a catastrophic outcome, DevOps leaders must be aware of contract risks that are easy to miss. Today, we’ll show you four, but be warned: there are more worth watching.
1. The “No Liability for Downstream Pipeline Failures” Clause
Most enterprise SaaS contracts contain a standard Limitation of Liability clause, capping the vendor’s financial responsibility to the amount paid for the software over the previous 12 months.
While this may be the standard, it becomes risky when applied to core DevOps infrastructure (e.g., CI/CD platforms, artifact repositories, or cloud orchestration tools). If a vendor outage or a compromised runner brings your entire deployment pipeline down for days, a standard cap means you only recover pennies on the dollar.
The Fix: Ensure that critical-path DevOps tools feature specialized liability carve-outs or higher liability caps for direct damages caused by service availability failures or vendor-side data corruption.
2. Overreaching Data Usage and Derivative AI Training Rights
Data is among the most precious currencies nowadays, especially for SaaS vendors. They need your “de-identified, anonymized metadata” to optimize their products or train machine learning models.
When your pipeline metadata, environment variables, system logs, and Infrastructure-as-Code configurations contain highly sensitive architectural blueprints, internal IP addresses, and proprietary code patterns, this is a huge compliance risk.
The Fix: Hire a team of AI lawyers to read every vendor contract and identify quiet language that gives third-party tools the right to use your data (even anonymized). Specialized lawyers, savvy in AI and data usage language, can also help design contracts that state your data is exclusive property and cannot be used for vendor product development or AI training.
3. The DPA Sub-Processor Cascading Risk
Each SaaS vendor contract comes with a Data Processing Addendum that outlines, among other things, who the vendor uses to process data. However, SaaS vendors change their infrastructure stacks frequently.
Every single infrastructure layer your vendor adds (e.g., switching their hosting from AWS to GCP, or routing analytics through a new third-party pipeline) introduces a new compliance boundary. If a vendor changes a sub-processor and your team hasn’t set up the architectural walls to restrict what data flows there, you can inadvertently violate your own customer DPAs.
The Fix: Actively collaborate with a team of commercial contract lawyers to design unbreakable rules that protect your data from landing into third-party hands. For better context, make sure your lawyers are up to speed with your engineering boundaries, like where your data lives, how fast your team can react to an outage, and what happens if you need to tear down the tool.
4. Vague Data Ingress/Egress Clause
Some contracts are deliberately vague about what happens with your data when you want to leave. These terms are usually defined in the Termination Assistance or Data Return clause, so read it carefully. Otherwise, you may end up having to pay an exorbitant data extraction fee.
The Fix: Use an AI contract analysis tool to scan the contract from top to bottom and identify any sketchy language or clauses. Also, design your own exit clause and include it in the contract. Specify that upon termination, the vendor must provide data extraction utilities or export your data in standard, open formats.
Don’t Sign What You Don’t Understand
Most of us just check Terms and Conditions and move on with our lives, but DevOps leaders don’t have this luxury. Of course, you shouldn’t spend your precious time reading contracts and trying to make sense of legalese. That’s what lawyers are for.
In today’s day and age, when everyone is thirsty for data and compliance regulations get stricter by the day, it’s essential to have access to adequate and reliable legal counsel. It’s worth the cost.

I’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked at Cotocus and regularly write about technology, travel, investing, health, product reviews, and digital marketing through my various platforms.
I publish technical articles at DevOps School, travel stories at Holiday Landmark, stock market insights at Stocks Mantra, health and fitness guidance at My Medic Plus, product reviews at TrueReviewNow, and SEO and digital marketing strategies at Wizbrand.
Find Trusted Cardiac Hospitals
Compare heart hospitals by city and services — all in one place.
Explore Hospitals

SaaS contracts deserve the same care as technical reviews. DevOps leaders should check data ownership, exit terms, and service limits before signing. Pay close attention to price changes and automatic renewals. Also, confirm how quickly the vendor must report security incidents. Keep a record of contract dates and review them before renewal. These steps can prevent costly surprises and reduce risks during a tool change.
One risk often missed in SaaS contracts is the operational side—when outages or vendor failures happen, unclear SLAs and exit plans can quickly become a real DevOps headache.