
NewRelic Complete Troubleshooting Guide
Troubleshooting Guide of NewRelic Java Agents No data appears (Java) Determine permissions requirements (Java) Gather troubleshooting information (Java) All hosts appear as localhost Error bootstrapping New Relic…
Understanding of Newrelic agent configuration file newrelic.yml vs newrelic.config
The New Relic agent reads its configuration from the newrelic.yml or newrelic.config. New Relic APM agent configuration options allow you to control some aspects of how the…
How to remove existing applications from the New Relic Dashboard?
Prerequisite You must be an Owner, Admin, or APM add-on manager on your account to remove an application If a New Relic agent is still sending data,…
What is Splunk Enterprise Security and How its best tool for SIEM?
What is SIEM and Why is it so Important?If you would like to know What is SIEM and Why is it so Important, Please refer this url….
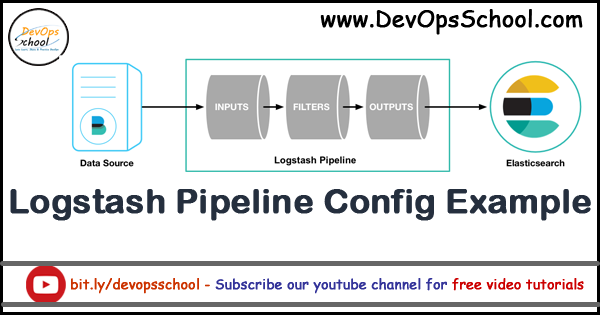
Example of Elastic Logstash pipeline input, filter and output
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
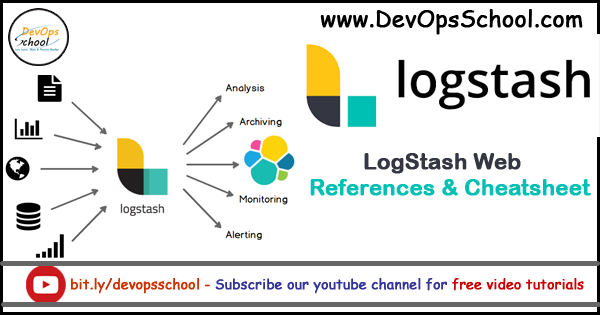
LogStash Web References & Cheatsheet
The grok filter is not easy to configure. We recommend testing your filters before starting Logstash using the grok debugger. https://grokdebug.herokuapp.com/ A rich list of the most…
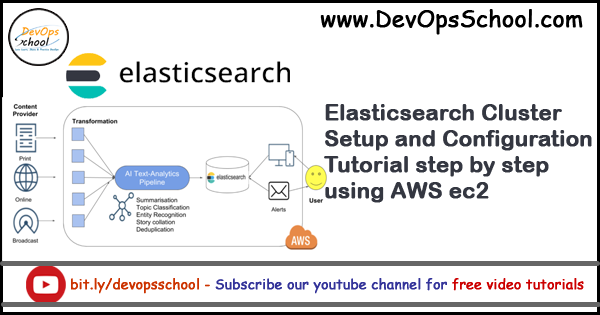
Elasticsearch Cluster Setup and Configuration Tutorial step by step using AWS ec2
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Elasticsearch QUERY Parameters Examples with Explanation
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Prometheus Pushgateway Installation, Configuration and Using tutorials.
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Prometheus Security and Authentication explained
[This tutorial is under developement] Prometheus does not directly support basic authentication (aka “basic auth”) for connections to the Prometheus expression browser and HTTP API. If you’d…
Recording rules and Alerting rules explained in Prometheus!!!
What is rules in Prometheus? Time series queries can quickly become quite complicated to remember and type using the Expression Browser in the default Prometheus User Interface….
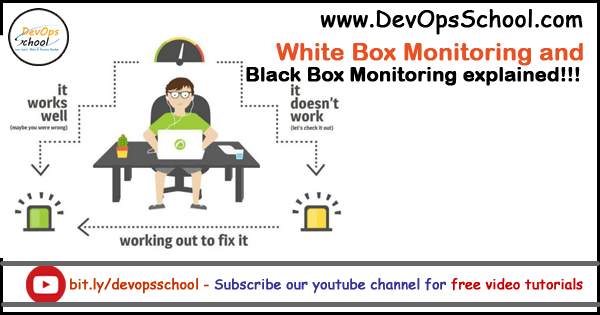
White Box Monitoring and Black Box Monitoring explained!!!
There are some basic principles and best practices for building successful monitoring and alerting systems. What is Monitoring?Collecting, processing, aggregating, and displaying real-time quantitative data about a…
Elasticsearch-ELK Errors and Solutions Database
Elastic Search Error – Node is started with node.data=false, but has shard data Elastic Search Error – max virtual memory areas vm.max_map_count [65530] is too low, increase…
ElasticSearch Error – filebeat – filebeat.yml – did not find expected key
Errors Solutions Check filebeat.yml: Only one file beat output is supported …check #output.elasticsearch is comments Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering…
ElasticSearch Error – filebeat – filebeat.yml – more than one namespace configured accessing ‘output’
Errors Answer Check output.logstash in filebeat.yml: should be uncommented. Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge,…
ElasticSearch Error – this can cause resize pauses and prevents mlockall from locking the entire heap
Error Message Solutions Setting the parameter -Xms to the same value of -Xmx in /etc/elasticsearch/jvm.options solved the problem 🙂 Thanks Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE,…
Elasticsearch Command Lines and their Usage Guide
elasticsearch elasticsearch-certgen elasticsearch-certutil elasticsearch-cli elasticsearch-croneval elasticsearch-env elasticsearch-env-from-file elasticsearch-keystore elasticsearch-migrate elasticsearch-node elasticsearch-plugin elasticsearch-saml-metadata elasticsearch-setup-passwords elasticsearch-shard elasticsearch-sql-cli elasticsearch-sql-cli-7.6.0.jar elasticsearch-syskeygen elasticsearch-users x-pack-env x-pack-security-env x-pack-watcher-env Rajesh KumarI’m Rajesh Kumar, a DevOps,…
Splunk Interview Questions and Answer Part – 4
Which file is used for role and mapping authorize.conf (Ans) authorizes.conf authentication.conf limits.conf You can not search the data in frozen stage of bucket True (Ans) False…
Splunk Interview Questions and Answer Part – 3
Of the following, which is the best description of Splunk? Splunk is a log collector. Splunk is a business intelligence tool. Splunk is operational intelligence that consumes…
Splunk Interview Questions and Answer Part – 2
Which port is the default forwarding port? 8683 8089 9997 (Ans) 8079 9907 9090 80 8080 Universal forwarders do not parse data. False True (Ans) Which port…
Splunk Interview Questions and Answer Part – 1
Where is the best place to get help with general Splunk questions? Splunk Answers (Ans) Stack Overflow Course Q and A Splunk is primarily a business intelligence…
How to enable Elastic Search REST API Accessible using IP Address?
By default http transport and internal elasticsearch transport only listens to localhost. If you want to access Elasticsearch from the host other than localhost then try adding…
Kibana 7.2 Install and configuration in RHEL 7/Centos
Install and Setup JDK 8+ Download and Install Kibana 7.X Configure Kibana 7.X How to start kibana service? Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud,…
How to use elastic search EC2 discovery plugin?
Problem To increase the performance in Elasticsearch, many times we add new nodes to Elasticsearch cluster and manually change the configuration file with new IP address, etc….
Elastic Search Error – Node is started with node.data=false, but has shard data
[2019-07-11T09:59:18,013][ERROR][o.e.b.Bootstrap ] [es-master01] Exception java.lang.IllegalStateException: Node is started with node.data=false, but has shard data: [/home/ec2-user/elasticsearch-7.2.0/data/nodes/0/indices/6XsNftnbSbOnzPK3wOKc 0w/0]. Use ‘elasticsearch-node repurpose’ tool to clean up at org.elasticsearch.env.NodeEnvironment.ensureNoShardData(NodeEnvironment.java:1065) ~[elasticsearch-7.2.0.jar:7.2.0] at…
Elastic Search Error – max virtual memory areas vm.max_map_count [65530] is too low, increase to at least [262144]
Errors [2]: max virtual memory areas vm.max_map_count [65530] is too low, increase to at least [262144] Solution To make it persistent, you can add this line: $…
Elastic Search Error – max file descriptors [4096] for elasticsearch process is too low, increase to at least [65535]
Elastic Search Error – max file descriptors [4096] for elasticsearch process is too low, increase to at least [65535] Solution Temporary to the current login session To…
How to create sample data to perform searches using elastic search?
Step 1 – Go to: http://www.json-generator.com/ Step 2 – Download and save as customers_full.json Step 3 – Open customers_full.json in sublimetext Remove the array brackets Find-Replace },{…
Elastic Search Error – The bulk request must be terminated by a newline
FIX – Add a New line in customers_full.json Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world…
ElasticSearch Error – illegal_argument_exception – Rejecting mapping update to type
########### COMMAND ################# ########### OUTPUT ########### Solution Multiple mapping types are not supported in indices created in 6.0 The ability to have multiple mapping types per index…