
Splunk Observability Cloud vs Splunk AppDynamics vs Splunk Cloud Platform
Here’s a clear and updated comparison between Splunk Observability Cloud, Splunk AppDynamics, and Splunk Cloud Platform, highlighting their purpose, strengths, and ideal use cases: 📦 Product Overview…
5-Day Program: Splunk for Email Security, SIEM & Endpoint Security
Program Title Splunk Security Operations Masterclass: Email Security, SIEM & Endpoint Detection Duration 5 DaysRecommended format: 6–7 hours per dayMode: Instructor-led + hands-on labs + final SOC…
AppDynamics Joins the Splunk Observability Portfolio
Based on the official information from Splunk’s June 2026 update, here’s a crystal-clear breakdown of the current relationship and distinction between Splunk AppDynamics and the Splunk Observability…
What is Splunk and use cases of Splunk?
What is Splunk? Splunk is a powerful data analytics and visualization platform designed for log management, monitoring, and real-time data analysis. It is widely used across industries…
Splunk Tutorials: Splunk Commands Reference
Here’s an updated table with example queries that utilize the respective Splunk commands: Splunk Command Description Example Query (Apache Log) search Retrieves events that match specific search…
Splunk FAQ
How do I create source types for data originating from Forwarders? The Splunk platform does not support data preview through universal forwarders. Use a full Splunk platform…
Splunk Tutorial: Install & Configure Heavy Forwarders
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorial: Install & Configure Universal Forwarders
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorial: Install & Configure Splunk Server
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorial: Adding More Data into it
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorials: App Deployment Server
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorial: Install & Configure Splunk Server (Indexer + Search Head + Universal forwarder)
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorials: Windows Query
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorials: Data Models
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorial: Lookup
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Command Line Reference
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Tutorials: Download Splunk & Universal Forwarder
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
Splunk Demo Tutorials
Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices. I have worked…
What is Splunk and How it works? An Overview and Its Use Cases
History & Origin of Splunk Rob Das and Eric Swan co-founded this technology in the year 2003 as a solution to all the questions raised while investigating…
What is Splunk SIEM and How it works? An Overview and Its Use Cases
History & Origin of Splunk SIEM The Splunk platform removes the barriers between data and action, empowering observability, IT and security teams to ensure their organizations are…
Top 50 Interview questions and Answers for Splunk SIEM
The Splunk is a technology that is used for searching, monitoring, picturing, and analyzing machine data on an actual source. It is a tool for log supervision…
Top Splunk interview questions and answers
What are the components of Splunk? There are 3 main components in Splunk: Splunk Forwarder, used for data forwarding. Splunk Indexer, used for Parsing and indexing the…
Collection of Splunk sample data
Link – https://github.com/devopsschool-demo-labs-projects/splunk-sample-data Rajesh KumarI’m Rajesh Kumar, a DevOps, SRE, DevSecOps, Cloud, and Platform Engineering expert passionate about sharing practical knowledge, real-world experiences, and industry best practices….
How to Specify time modifiers in Splunk search?
When searching or saving a search, you can specify absolute and relative time ranges using the following time modifiers: earliest=time_modifier latest=time_modifier Examples of relative time modifiers Examples…
How to filter out specific sources, sourcetypes, and hosts in Splunk?
Problem:How to filter out specific sources, sourcetypes, and hosts from displaying on my Search Summary page in Splunk? Sample Data – https://www.devopsschool.com/tutorial/splunk/labs/sample-data/earthquake/all_month_earthquakes.csv Including or excluding or filter…
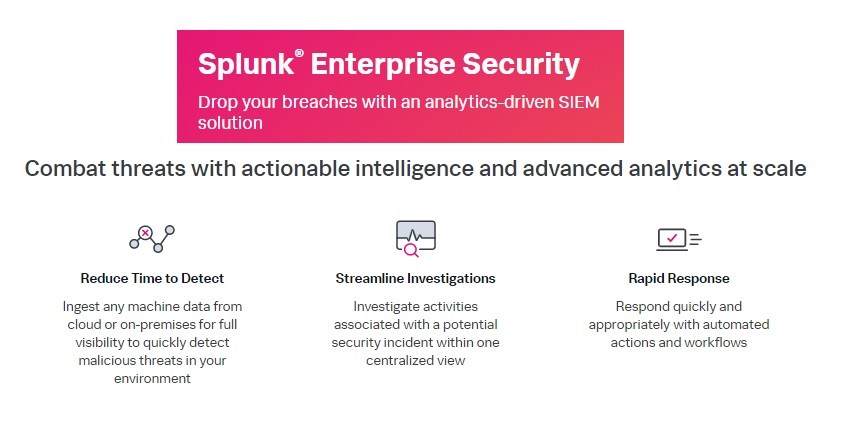
What is Splunk Enterprise Security and How its best tool for SIEM?
What is SIEM and Why is it so Important?If you would like to know What is SIEM and Why is it so Important, Please refer this url….
Splunk Interview Questions and Answer Part – 4
Which file is used for role and mapping authorize.conf (Ans) authorizes.conf authentication.conf limits.conf You can not search the data in frozen stage of bucket True (Ans) False…
Splunk Interview Questions and Answer Part – 3
Of the following, which is the best description of Splunk? Splunk is a log collector. Splunk is a business intelligence tool. Splunk is operational intelligence that consumes…
Splunk Interview Questions and Answer Part – 2
Which port is the default forwarding port? 8683 8089 9997 (Ans) 8079 9907 9090 80 8080 Universal forwarders do not parse data. False True (Ans) Which port…