
ElasticSearch Error – illegal_argument_exception – Rejecting mapping update to type
########### COMMAND ################# ########### OUTPUT ########### Solution Multiple mapping types are not supported in indices created in 6.0 The ability to have multiple mapping types per index…
ElasticSearch Error – Content-Type header [application/x-www-form-urlencoded] is not supported
To fix this, add curl option -H ‘Content-Type: application/json’. This error is due to strict content-type checking introduced in ElasticSearch 6.0 Solution Rajesh KumarI’m Rajesh Kumar, a…
Splunk frequently asked questions!!!
Question – How often does the forwarder send data to indexer?Answer – The forwarder sends data immediately when it becomes available. There is no certain interval that…
Where can I practice splunk search commands for free?
For newbies Splunk has provided Splunk free online sandbox where you can try splunk and practice on it. Below is link for splunk online sandbox.You need to…
Understanding the Update API in Elasticsearch
The update API allows to update(also allows to delete, or ignore the operation). a document based on a script provided. The operation gets the document from the…
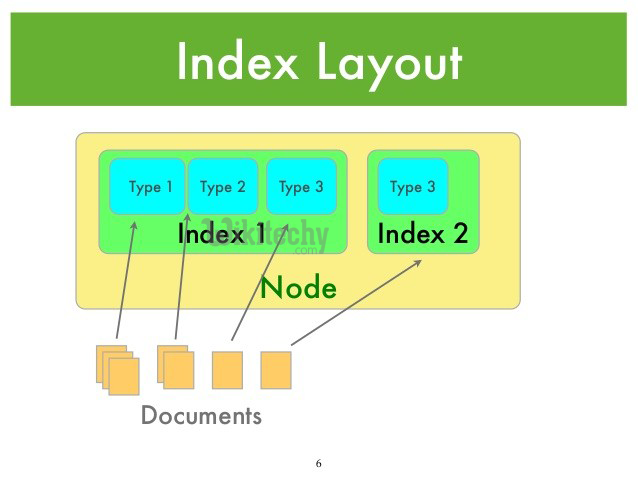
Understanding Elasticsearch Index Mapping & Schema
A schema is a description of one or more fields that describes the document type and how to handle the different fields of a document. The schema…
Find out elastic Search health using _cat/health
To check elasticsearch cluster health by using (CURL) and Cluster API “cat” provieded by elasticsearch The cat API print the info in JSON format, compact and aligned…
Understanding Elasticsearch Keywords and Terminology
Understanding Elasticsearch Keywords and Terminology Elasticsearch Terminology Description Cluster “A cluster is a collection of one or more nodes (servers) that together holds your entire data and…
Crash Course of Elasticsearch in 10 mins
What is Elasticsearch? Elasticsearch is fast, horizontally scalable open source search engine. It provides HTTP API for storing and indexing JSON documents and with default configuration it…
Elasticsearch Web References & Cheatsheet
Elasticsearch official documentation https://www.elastic.co/guide/en/elasticsearch/reference/6.x/index.html Very good Elasticsearch Guide on Github https://github.com/dzharii/awesome-elasticsearch Elasticsearch Official forum https://discuss.elastic.co/ Stackoverflow elasticsearch handlers http://stackoverflow.com/questions/tagged/elasticsearch Jolicode elasticsearch Cheatsheet http://elasticsearch-cheatsheet.jolicode.com/ Elasticsearch DevOpsSchool reference https://www.devopsschool.com/blog/category/elastic-stack/…
Web GUI tools for Elasticsearch cluster
elasticsearch-head is a web front end for browsing and interacting with an Elastic Search cluster. There are multiple ways of running elasticsearch-head. Running as a plugin of…
Understanding REST HTTP method – GET, POST, PUT, HEAD, DELETE in Elasticsearch
REST (Representational State Transfer) was introduced and defined in 2000 by Roy Fielding in his doctoral dissertation. REST is an architectural style for designing distributed systems. It…
What are the method to interact with Elastic Search?
Elasticsearch provides official clients for several languages—Groovy, JavaScript, .NET, PHP, Perl, Python, and Ruby—and there are numerous community-provided clients and integrations, all of which can be found…
Install and Configure Grafana in Ubuntu and Debian
This Tutorial is Deprecated and New Version of Tutorial you can find here – CLICK HERE Install and Configure Grafana in Ubuntu and Debian Step 1 –…
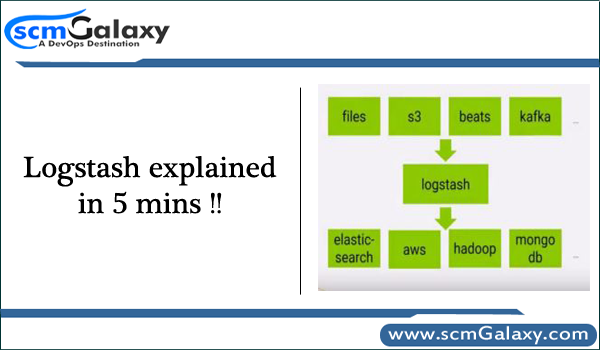
Logstash explained in 5 mins
What is Logstash? Logstash is an open source, server-side data processing pipeline that ingests data from a multitude of sources simultaneously, transforms it, and then sends it…
Log Management Tools using splunk and other alternatives
Splunk Splunk (the product) captures, indexes and correlates real-time data in a searchable repository from which it can generate graphs, reports, alerts, dashboards and visualizations. Splunk aims…
Application Performance Monitoring Tools
New Relic New Relic is an all-in-one web and mobile application performance management provider for the cloud and the datacenter. It provides 24×7 real user monitoring and…
IT infrastructure and Cloud Monitoring Tools
Why Cloud Monitoring is essential? Security SLA management Capacity planning Resource management Trouble shooting Performance management Open Source Tools for Cloud Monitoring Zenoss Hyperic Gangila Nagios OpenNMS…
A Comparison of Nagios, Zenoss and Zabbix
Source – OpenSource Feature Nagios Zenoss Zabbix Basic features (CPU, disk, memory) YES YES YES Auto discovery Partial YES Partial License Free Free Free Inventory Support No Free…

How to Start and Stop Nagios Core | Nagios Tutorial
Starting Nagios Core Init Script: The easiest way to start the Nagios Core daemon is by using the init script like so: /etc/rc.d/init.d/nagios start Manually: You can…

Steps to Start-Stop Nagios XI Server | Nagios XI Tutorial
How to start and stop Naxios XI Server? How to stop Naxios XI Server? service nagiosxi stop service npcd stop service ndo2db stop service nagios stop service…

Step by step procedures to Install Nagios agent in Linux
Step by step procedures to Install Nagios agent in Linux > cd /tmp > mkdir software > cd software > yum install wget > wget https://assets.nagios.com/downloads/nagiosxi/agents/linux-nrpe-agent.tar.gz >…

Step by step procedures to Install Nagios XI Server in Centos 7
Step by step procedures to Install Nagios XI Server in Centos 7 #Update your centos os > yum install update > yum install wget # to install…